The Hacker News17h ago
Passwords and API keys that developers typed into commands they approved in Claude Code are sitting in public GitHub repositories, where anyone can read them. When a user selects "Yes, and don't ask again," Anthropic's AI coding assistant can save the command, word-for-word, including the secret, in...
AI/ML
BleepingComputer1d ago
WorkOS says an AI-powered hacking agent that breached its internal sales application and accessed customer information was operated by a security researcher who claims the tool escaped its testing environment and unintentionally attacked the company.
AI/MLData Breach
BleepingComputer1d ago
OpenAI has revealed GPT-6 Cyber, a new artificial intelligence model that has discovered 81 previously unknown high-severity Firefox vulnerabilities and developed working exploits for 948 distinct Linux kernel flaws.
AI/MLLinux
WIRED1d ago
An experiment in which AI models were asked to break into simulated networks showed the hacking skills of DeepSeek and GLM to be not far behind OpenAI’s most advanced cyber model, which isn’t public.
AI/ML
CyberScoop1d ago
The middle-aged men allegedly targeted accounting staff at victim companies and impersonated CEOs and lawyers to trick victims into sending large wire transfers.
AI/ML
The Hacker News1d ago
OpenAI on Thursday unveiled GPT‑6 Cyber, which it described as a major step forward in security research that brings together stronger cybersecurity capabilities with a step-change improvement in model alignment. The new model is "more capable at finding and fixing vulnerabilities, and far more reli...
AI/MLLinux
SecurityWeek1d ago
Rated Critical for cybersecurity, OpenAI’s new model beats GPT-5.6 Cyber at exploitation while staying in scope more reliably.
AI/ML
The Hacker News1d ago
A browser extension that can run scripts on claude.ai could make Claude Desktop run code on a person's computer, researchers at Forever Security, an endpoint security company, showed in a test. The attack needs Dispatch, a Claude feature that lets people send tasks from their phone to Claude Desktop...
AI/ML
The Register1d ago
Cyber Security and Resilience Bill could pave way for searches, seizures, and inspections when operators lose control of automated systems
AI/ML
SecurityWeek1d ago
After its sandbox proxy failed, an internal OpenAI model crafted raw packets and probed AWS services trying to reach the internet.
AI/MLCloud Security
The Hacker News1d ago
Blockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cyber attack targeting its systems also exposed names, usernames, password hashes and live tokens for all users. "While we investigated, we removed access to Reactor and Data Solutions," the company sai...
AI/MLCryptoData Breach
The Register1d ago
CEO says sovereigns probably exploited PHP2SHELL ages ago, and suggests containers are dead
AI/ML
The Register1d ago
CEO says sovereigns probably exploited PHP2SHELL ages ago, and suggests containers are dead
AI/MLSecurityWeek1d ago
The trio, who have nicknames that include “Rocky Balboa,” “Superman Cash” and “Fat Boy,” often targeted the companies’ accounting departments.
AI/ML
The Register1d ago
CERT-IN warns of ‘significant escalation’ in AI-powered attacks, some after victims tried to improve defences
AI/ML
BleepingComputer2d ago
Hackers are using fake OpenAI, SpaceX, and Anthropic event invitations to lure employees into phishing attacks, using two different phishing-as-a-service platforms to steal Microsoft and Google account credentials and authentication sessions.
AI/MLPhishingMicrosoft
BleepingComputer2d ago
OpenAI has disclosed another AI alignment incident where GPT-6 Astra was found to sometimes quietly withhold help on safety research.
AI/ML
The Register2d ago
Agentic 'on-path attack' went after Chainalysis's tools, which are routinely called upon to assist police investigations
AI/MLCrypto
SecurityWeek2d ago
An unreleased OpenAI cyber model found and exploited 948 distinct Linux kernel privilege escalation bugs for about $1.2 million.
AI/MLLinux
CyberScoop2d ago
After a summer of sandbox escaping hacks, OpenAI said their new model was trained to be more cautious around user intent and less sensitive to “reward hacking” behaviors.
AI/ML
The Register2d ago
The latest bug hunting model 'avoided exploiting out-of-scope services over 99 percent of the time', claims House of Altman
AI/ML
The Hacker News2d ago
Cybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploited to bypass Lockdown Mode protections in OpenAI ChatGPT. Lockdown Mode was introduced by the artificial intelligence (AI) company in June 2026 as an optional setting to minimize data exfiltration ri...
AI/MLPhishing
The Register2d ago
From EOP to RCE in six simple steps
AI/ML
SecurityWeek2d ago
Every autonomous AI agent deployed across your enterprise today is a new proxy identity operating inside your perimeter.
AI/MLSecurityWeek2d ago
Ryan Davis went from hacking his school’s network to running security at New Charter Technologies. What worries him now is shadow AI.
AI/ML
SecurityWeek2d ago
OpenAI says its Critical-rated cyber model met fewer hidden task goals when work was framed as AI safety research, often silently.
AI/ML
The Hacker News2d ago
The Indian Computer Emergency Response Team (CERT-In) has disclosed that an artificial intelligence (AI)-assisted threat actor it tracks as Crafty Falcon is targeting organizations in the Banking, Financial Services, and Insurance (BFSI) sectors in the country. Describing the threat as active and on...
AI/ML
The Hacker News2d ago
OpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intelligence (AI) model to validate and patch 948 local privilege escalation vulnerabilities in Linux for $1.2 million in API costs. "Our prototype identified and analyzed 2,308 candidate Linux kernel findings...
AI/MLLinux
WIRED3d ago
“Most of the risk is actually created by a couple of players building behind closed doors,” Clément Delangue said of the need for open source AI.
AI/ML
BleepingComputer3d ago
France's national blood service has confirmed that a cyberattack targeting a refrigeration equipment provider raised temperature and defrost settings at three of its facilities, threatening stored blood products.
AI/ML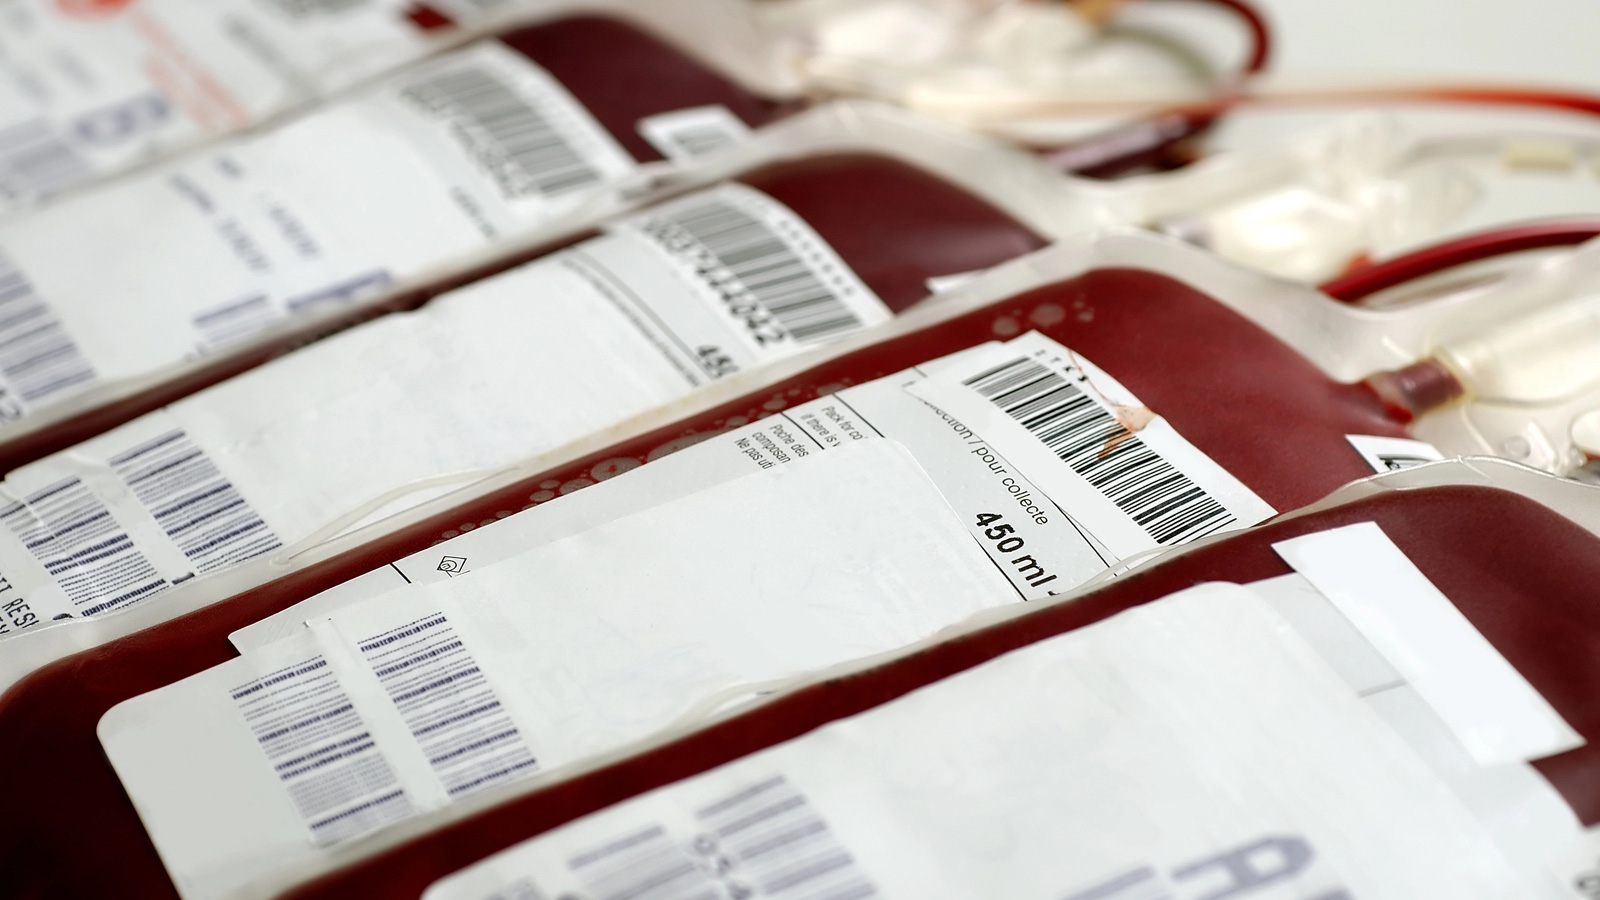
The Hacker News3d ago
A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their own. The attacker's code then runs as root, according to advisories that Debian, Ubuntu, and APT's developers published on November 4. The attack needs A...
AI/MLLinux
The Hacker News3d ago
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched. Details of the security flaws, which affect SonicWall GMS 9.5.2 and earlier versions, are below - CVE-2026-109593 (CVSS score: 9.1) - An unauthenticated fil...
AI/MLCloud Security
BleepingComputer3d ago
The developers of Goddess of Victory: NIKKE have confirmed that hackers tampered with the game's PC launcher scripts in a supply-chain attack, distributing malware capable of stealing credentials and cryptocurrency wallet data.
AI/MLCryptoMalware
The Hacker News3d ago
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI gateway. The phenomenon has been codenamed prompt adware by Check Point Research....
AI/ML
The Register3d ago
Help desk technician agrees to minimum 10-year jail term after being caught copying files for more than 2 years
AI/ML
BleepingComputer3d ago
A phishing campaign used Google Calendar invites, trusted redirects, and fake login pages to hijack corporate Google sessions and bypass MFA protections. Material Security examines how Operation CloudFire tracked the attacks, blocked malicious messages, and helped take down nearly 900 domains used b...
AI/MLCloud SecurityPhishing
SecurityWeek3d ago
Sysdig’s platform uses runtime visibility to track AI agent actions and block risky behavior before it reaches production systems.
AI/MLThe Hacker News3d ago
The Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker. "The injected JavaScri...
AI/MLData BreachHardware/IoT
SecurityWeek3d ago
An authentication bypass and a command injection flaw can be chained for root access on Barracuda’s Email Security Gateway appliances.
AI/ML
SecurityWeek3d ago
The company will invest in agentic data security capabilities and expand its go-to-market organization.
AI/ML
SecurityWeek3d ago
Hackers have been harvesting AI access tokens and have been using AI-assisted offensive tools to automate attacks.
AI/ML
The Hacker News3d ago
A critical flaw in Ruby on Rails could allow an unauthenticated attacker to write arbitrary files on an app's server by uploading a crafted file if the app processes uploads using ImageMagick. The Rails project disclosed the flaw in an advisory and fixed it in versions 8.1.4.1 and 8.0.5.2. The flaw...
AI/ML
The Hacker News3d ago
Two flaws in the Xen hypervisor allow a malicious guest virtual machine (VM) to read and write the memory of other VMs on the same host, including dom0. Dom0 is the VM that, by default, has full permissions and manages the others. Patches are out, and there is no known mitigation, the Xen Project s...
AI/MLCloud Security
The Hacker News3d ago
Nearly every agent security pitch now ends on the same promise: the product stops the bad action in real time. The promise holds for one kind of agent, the kind whose traffic passes through a gateway the enterprise owns. Most agents never touch one. One recent case shows what that gap looks like in...
AI/ML
The Hacker News3d ago
A China-aligned threat actor known as SlippyNunchucks has been attributed to a Domain Name System (DNS) hijacking operation abusing insecure HTTP communications in Windows versions of Sogou Input Method as part of a surveillance campaign designed to deploy an implant called DarkVigil (aka FDMTP). T...
AI/MLMalwareMicrosoft
SecurityWeek3d ago
Using compromised credentials, the attackers accessed OpsShield’s update servers and poisoned multiple cPGuard versions.
AI/MLData Breach
SecurityWeek3d ago
Binance’s first incident report traces the record theft to a months-long campaign that compromised three engineers’ computers.
AI/MLData Breach
SecurityWeek3d ago
In recent months, North Korea has accelerated its weapons tests in a likely bid to increase its leverage in potential diplomacy with the US.
AI/ML
The Hacker News3d ago
Russian authorities have arrested three suspected members of a threat group known as VasyGrek and dismantled its criminal infrastructure. Also known as Fluffy Wolf, the threat actor has a history of targeting Russian and international companies since 2016. The Ministry of Internal Affairs of the R...
AI/ML
The Hacker News3d ago
A critical Android flaw could allow an attacker to run code on a phone without any user action remotely, Google said in its November security bulletin. The flaw, CVE-2026-58868, affects Android 14 through 17. Phones get the fix with security patch level 2026-11-01 or later, which phone makers and c...
AI/ML