BleepingComputerJust now
ASUS released Control Center Express v1.7.29 to fix three critical vulnerabilities that could let remote attackers gain administrative control of the management console and the devices it manages.
The RegisterJust now
First service outages, then data breaches…what's next?!
The Register3h ago
Ransomware group sets a deadline for the chipmaker to pay up - or see its data leaked
RansomwareData Breach
The Hacker News3h ago
The easiest way to fool someone is to give them something they already expect. A job offer. A message about a service outage. A familiar app. Nothing looks strange at first. And that's the problem. This week's stories show how ordinary things are being used to steal data, spread malware, and get peo...
AI/MLMalware
CyberScoop4h ago
Michael LoSapio, the Palantir executive and Trump administration nominee for CISA, sparred with Democrats on the committee over who won the 2020 election, Jan. 6 and more.

WIRED5h ago
The company’s alternate-universe internet serves as a massive sandbox that allows the Chrome team to properly train AI browsing agents—without the risk of them going rogue.
AI/ML
The Hacker News5h ago
PHP's default file-based session storage can be made to return objects an attacker chose, by cutting off a session write at the right moment. When combined with a second weakness, such as a suitable gadget chain in the app, those objects can allow the attacker to run code on the server. Today's PHP ...

BleepingComputer5h ago
The PHP development team released security updates addressing 18 vulnerabilities, including critical flaws that could allow unauthenticated attackers to remotely execute code on vulnerable servers.
The Register5h ago
DoJ claims suspect part of 4-month operation to steal secrets, surveil employees
SecurityWeek6h ago
Successful exploitation could allow attackers to crash the worker process and execute code with the PHP worker’s privileges.
BleepingComputer7h ago
Ransomware attacks often involve credential theft, lateral movement, and attempts to disable security controls long before encryption begins. Acronis examines five warning signs that can help defenders detect intrusions earlier, contain malicious activity, and protect critical systems and backups.
RansomwareData Breach
BleepingComputer7h ago
Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root access.
Linux
The Hacker News7h ago
The PHP Foundation has released security updates to address multiple critical security flaws that could be exploited to achieve remote code execution on affected deployments, including CVE-2026-115560. The list of vulnerabilities is as follows - CVE-2026-115560 (CVSS score: 9.2) - An improper input ...

The Hacker News7h ago
Under specific conditions, a critical vulnerability in Drupal core can allow an attacker without login credentials to use the built-in installer to attempt to reinstall a site. That can lead to a site takeover or remote code execution, and the project rates the vulnerable configurations as uncommon....

SecurityWeek7h ago
Nvidia says it has found no indication that its systems were compromised after the Gentlemen ransomware group listed the company as a victim.
Ransomware
SecurityWeek8h ago
Attackers hacked clustered Cisco Expressway devices at a Russian organization and prepared tooling for lateral movement.
Zero-Day
BleepingComputer8h ago
The Drupal Security Team has patched a critical remote code execution vulnerability that can let attackers take over vulnerable sites.
SecurityWeek9h ago
The company will use the funds to accelerate the development and distribution of its security platform.

SecurityWeek10h ago
Lower costs, data privacy, and greater control are driving open-weight AI adoption, but many organizations are not addressing the risks that come with it.
AI/ML
The Hacker News10h ago
One of the early targets of PHP2Shell exploitation was the firewall. On October 28, Palo Alto Networks confirmed that attackers were exploiting the two PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, against PAN-OS management interfaces exposed to the internet. Both flaws let anyone execut...

BleepingComputer10h ago
Microsoft is developing a new Edge security feature to reduce the attack surface by disabling the WebGL, WebGL2, and WebGPU APIs.
Microsoft
The Register10h ago
Minister calls notification delay 'not acceptable' after October attack on Irish banking player Wellington IT came to light in November

SecurityWeek11h ago
The security updates resolve critical and high-severity issues leading to authentication bypass, remote code execution, and privilege escalation.
BleepingComputer11h ago
Microsoft has shared a workaround for installation and launch issues affecting Office and third-party applications after installing this month's Windows 11 hotpatch.
Microsoft
SecurityWeek11h ago
The five NGINX2Root vulnerabilities could allow remote, unauthenticated attackers to execute arbitrary code.
Zero-Day
The Register11h ago
Don't leave your credentials out in public, where any visitor can see them.
The Hacker News12h ago
N-able on Wednesday disclosed that unknown threat actors gained unauthorized access to one of the servers in the Mail Assure and Spam Experts Hosted Cloud, causing it to disable management interfaces and APIs. "We have taken steps to mitigate the threat and are continuing to harden our services to r...
Cloud SecurityData Breach
BleepingComputer12h ago
NVIDIA is investigating claims of a security breach after the Gentlemen ransomware group has added the company to its dark web data leak site.
RansomwareData Breach
SecurityWeek12h ago
GreyNoise, WatchTowr and Cloudflare report probing and exploit attempts, while Cisco, Elastic, Red Hat and Siemens detail impact.
Linux
The Hacker News13h ago
Ruby contains seven memory-safety flaws in its regular expression engine and its string case-conversion code. For five of them, its maintainers say, proof-of-concept exploits, or PoCs, have shown that crafted input can run code on the machine. "We are aware of PoCs that prove some of them can be use...
Zero-Day
The Hacker News13h ago
Low-privilege database accounts that cannot read a single application table can still be used to run code on the database server itself, a researcher has shown, by reaching memory-corruption bugs in the engine code behind ordinary SQL. The exploits, published yesterday, are the researcher's proofs o...

The Hacker News14h ago
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added four vulnerabilities impacting Synology DiskStation Manager (DSM), BerriAI LiteLLM, Apache Axis, and Vanderbilt University Research Electronic Data Capture (REDCap) to its Known Exploited Vulnerabilities (KEV) catalo...
Ransomware
SecurityWeek14h ago
Affecting the session upload progress, CVE-2026-115560 was publicly disclosed two days after PHP2Shell patches landed.
The Hacker News17h ago
The maintainers of the PHP programming language on Wednesday issued an advisory announcing an upcoming security release that addresses critical flaws. The release is scheduled for November 19, 2026, between 2 and 2:30 p.m. UTC. "These releases are part of PHP's regular four-week release cycle and wi...

SecurityWeek18h ago
The all-stock deal will give the cybersecurity company a platform for fine-tuning and running open-weight AI models in public and sovereign clouds.
AI/ML
BleepingComputer22h ago
Ukrainian authorities, working with the FBI, have arrested four suspected members of an international ransomware organization linked to more than $40.5 million in ransom payments from at least 28 companies worldwide.
Ransomware
The Register23h ago
At least one dangerous RCE bug will get a fix on Thursday

The Register23h ago
At least one dangerous RCE bug gota fix on Thursday
The Register1d ago
Open source NGINX joins patchapalooza
AI/ML
CyberScoop1d ago
But cyberattacks aren’t directly to blame, Trump administration officials said.
AI/ML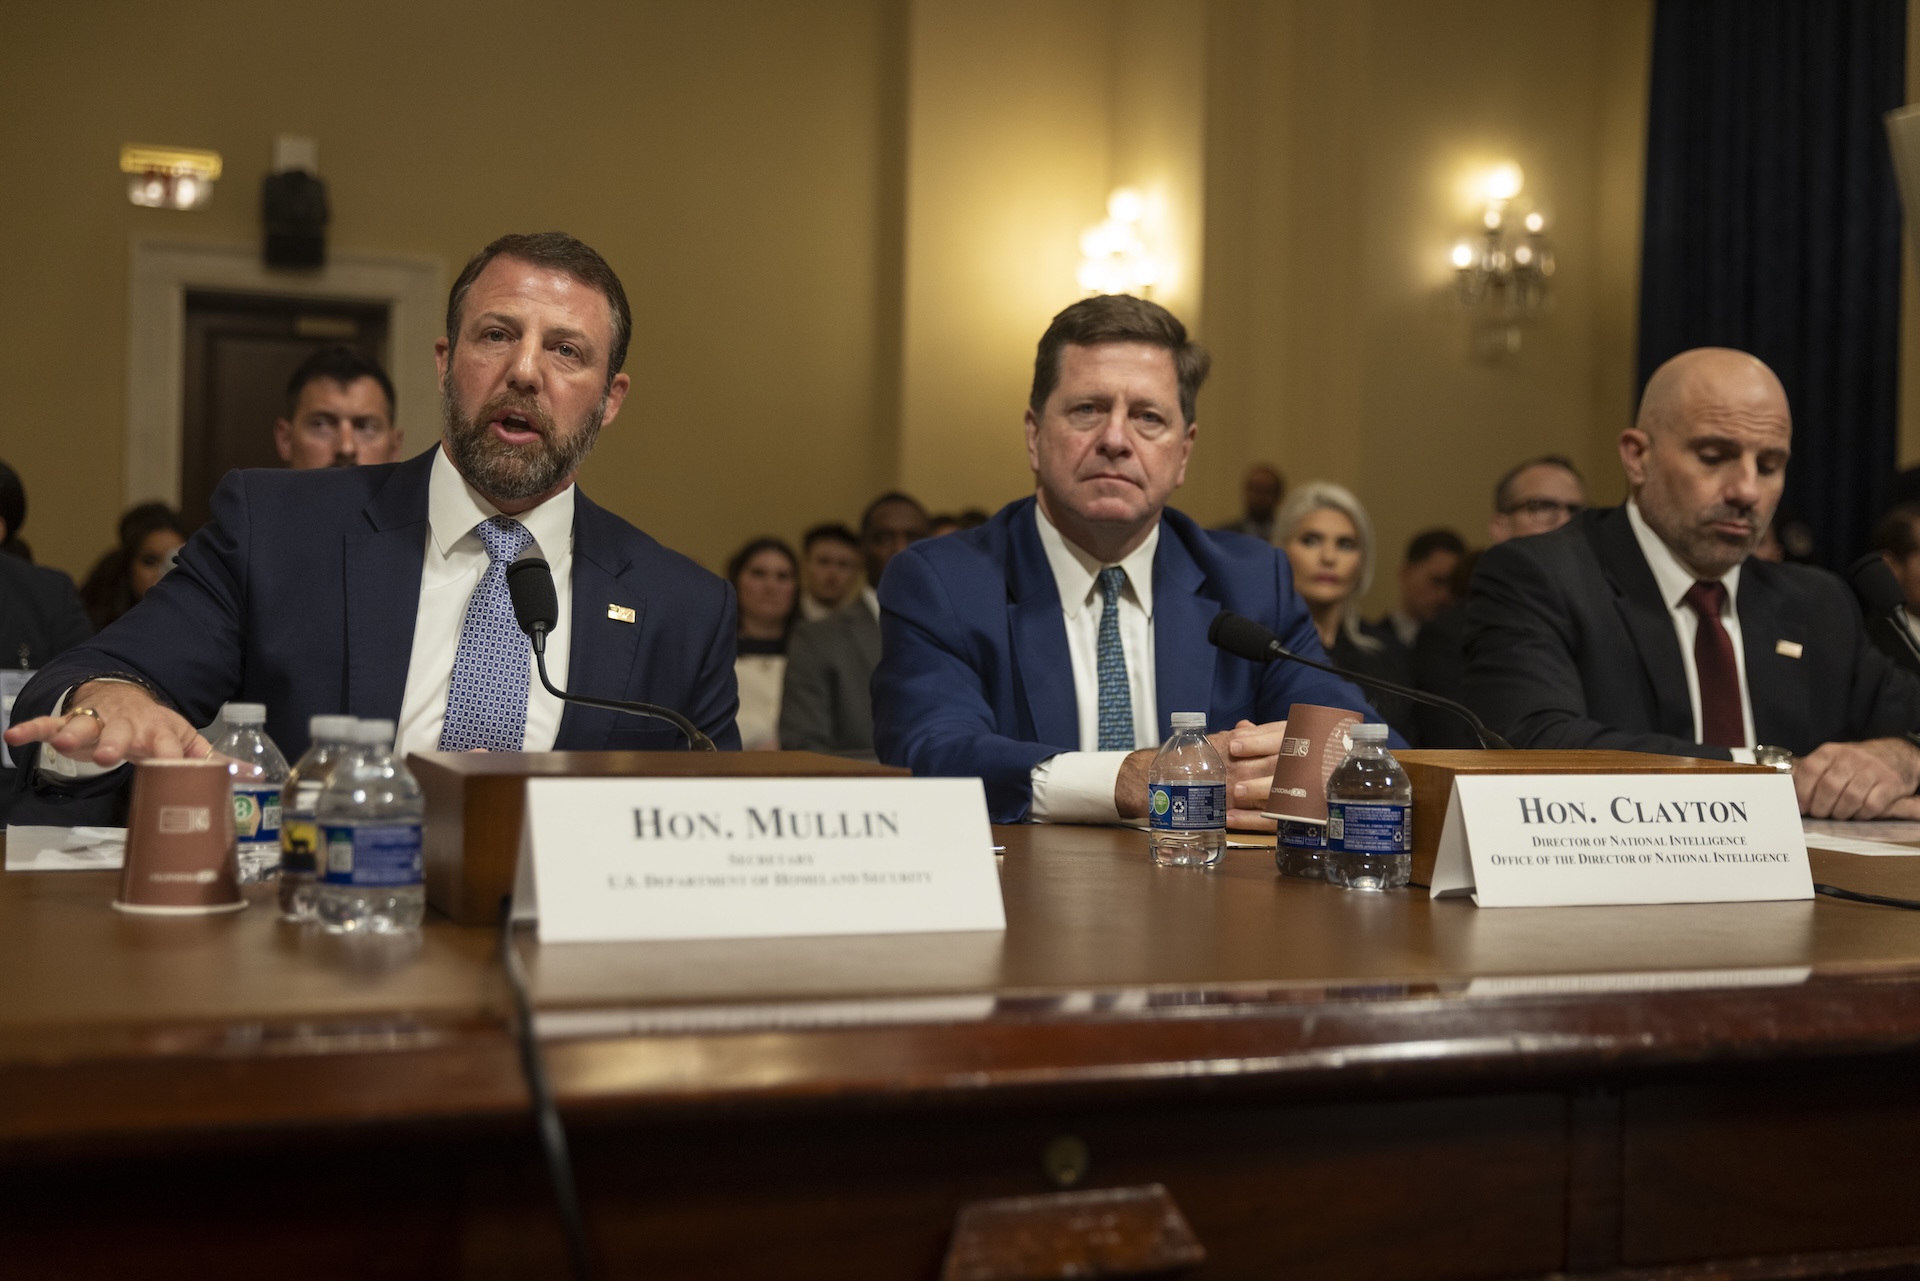
BleepingComputer1d ago
Coinbase says it blocked $4.7 million in cryptocurrency transfers to scammers promoting a fake giveaway using an AI-generated deepfake of Elon Musk during a Tesla livestream that attracted more than 500,000 viewers.
AI/MLCrypto
BleepingComputer1d ago
A reported cyberattack on Wellington IT has exposed sensitive information belonging to members of 50 credit unions, the majority of which are located in Ireland.
Data Breach
CyberScoop1d ago
Confirmation would give Republicans a 3-1 majority on the FCC. Meanwhile, the fates of multiple bipartisan cyber bills are in limbo after Democrats no-showed the markup hearing.
WIRED1d ago
A pair of serious vulnerabilities in the CreditNirvana platform would have allowed attackers to access troves of detailed sensitive information, including emails, texts, and credit reports.
AI/ML
CyberScoop1d ago
Researchers just dropped five NGINX exploits, including one that chains an HTTP/2 bug with a kernel flaw to seize the machine behind the web server.